list_projects()

Projects

Open-source tools I build and maintain for Microsoft Intune, Entra ID and Defender.

ship("DUDE Manager")released

Deterministic user → device group sync for Microsoft Intune.

Intune assigns policies to device groups. Organizations are structured around user groups. There is no native way to keep the two in sync.

DUDE maps user groups to device groups and keeps membership in sync on a schedule, as an Azure Function with Managed Identity. A PowerShell WPF GUI handles deployment, configuration, monitoring and posture review.

Open source · MITPowerShell 7.4+Azure FunctionsManaged IdentityGraph v1.0
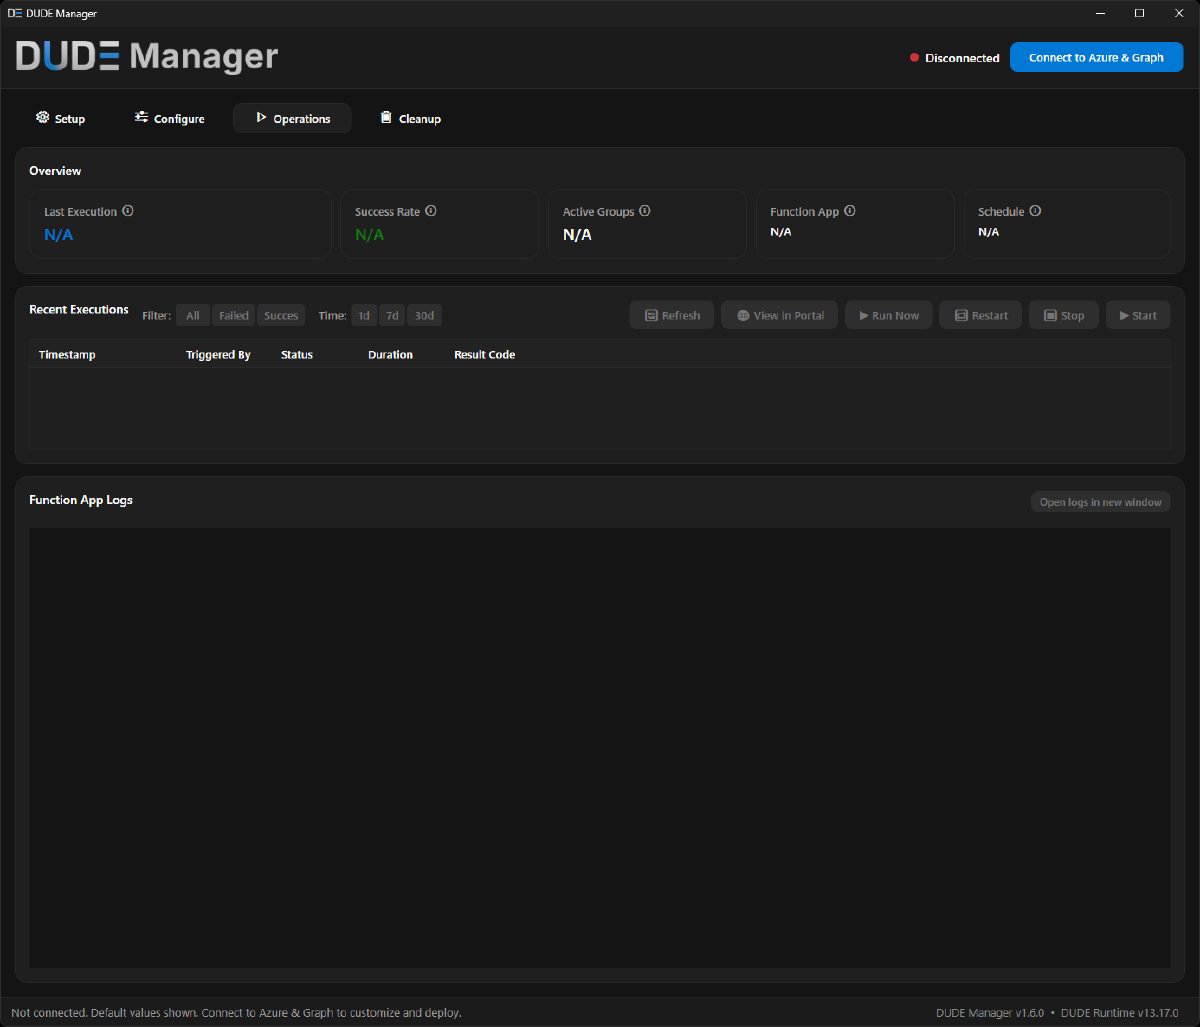
Operations — executions, status and live logs

Why it's built this way

Nested groups

Transitive membership, so sub-groups and their devices are included.

Fail-closed by default

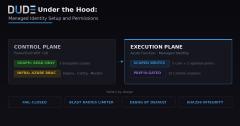
Group prefix allowlists, blast radius limiter, and new deployments start in read-only WhatIf mode.

Least privilege

No shared credentials. Runtime writes go through the Function App's Managed Identity.

Posture snapshot

Read-only checks and redacted evidence for security review and least-privilege drift.

Scoped admin

Optional sync to Administrative Units and Defender for Endpoint device tags.

Safe operations

Validate before write, privileged group detection, and WhatIf before any cleanup.

Inside the GUI

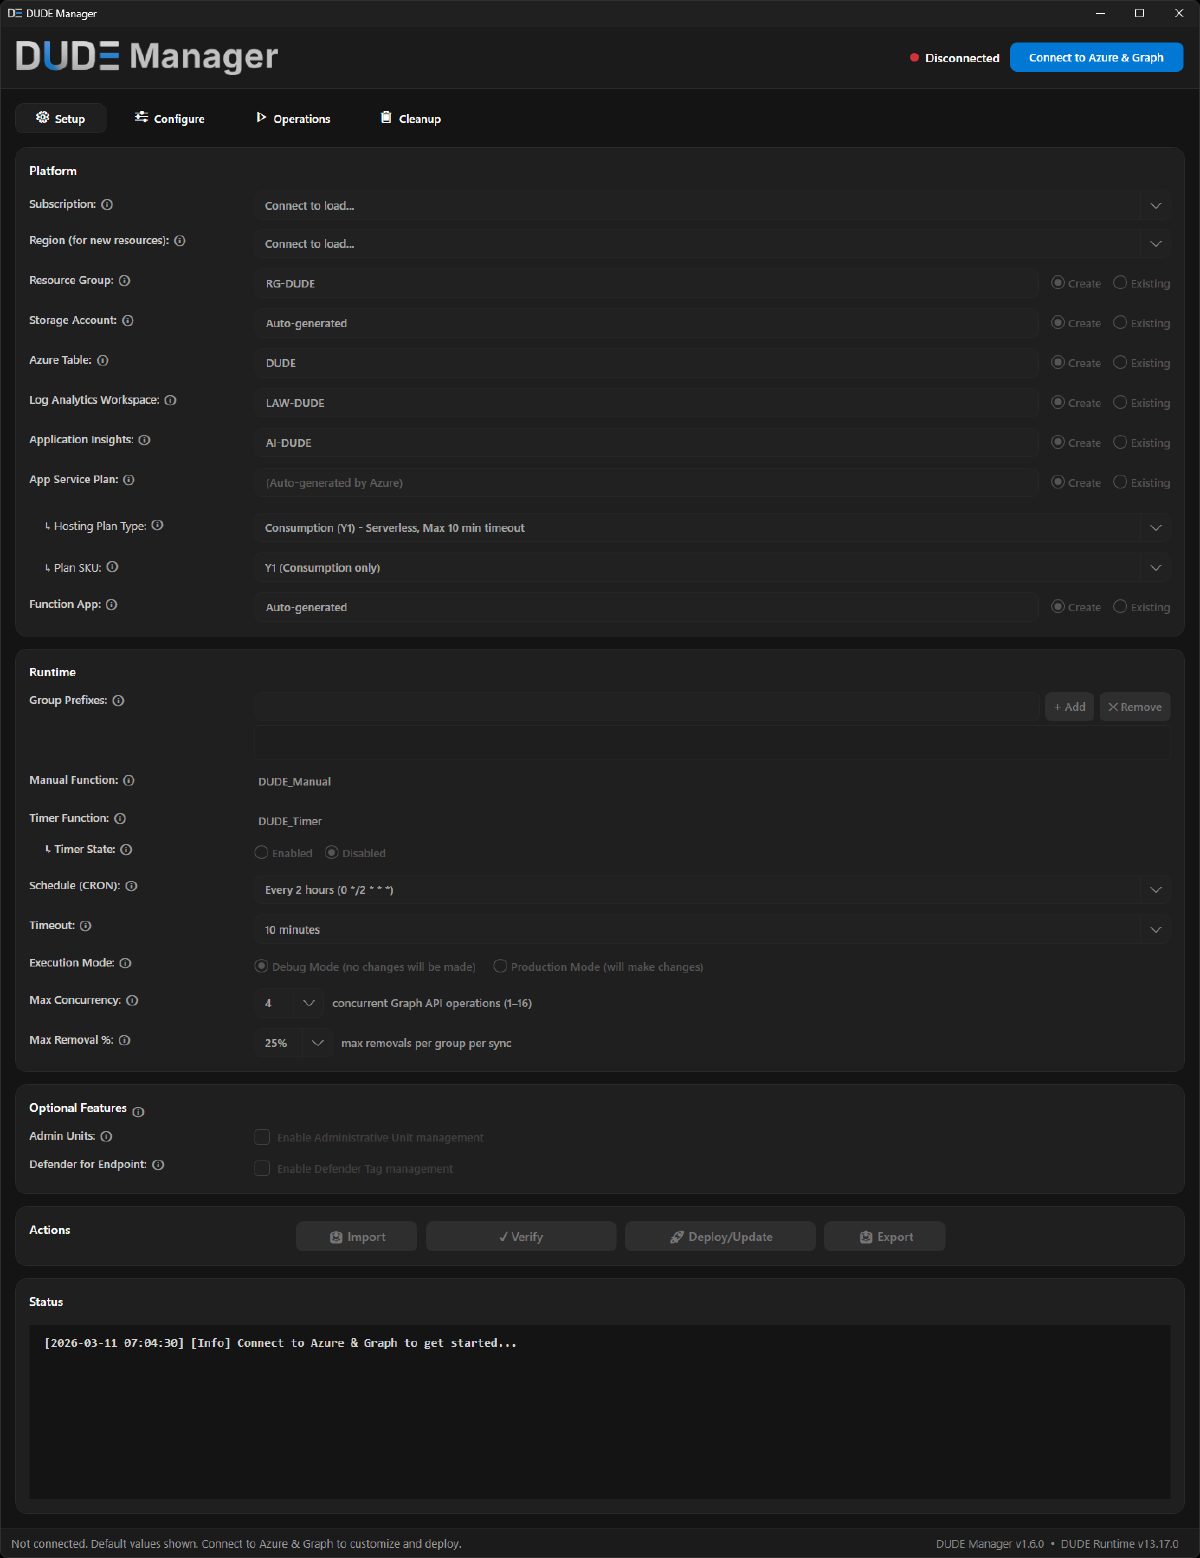
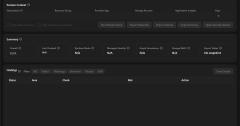
Screenshots show disconnected or sanitized states — no live tenant data.

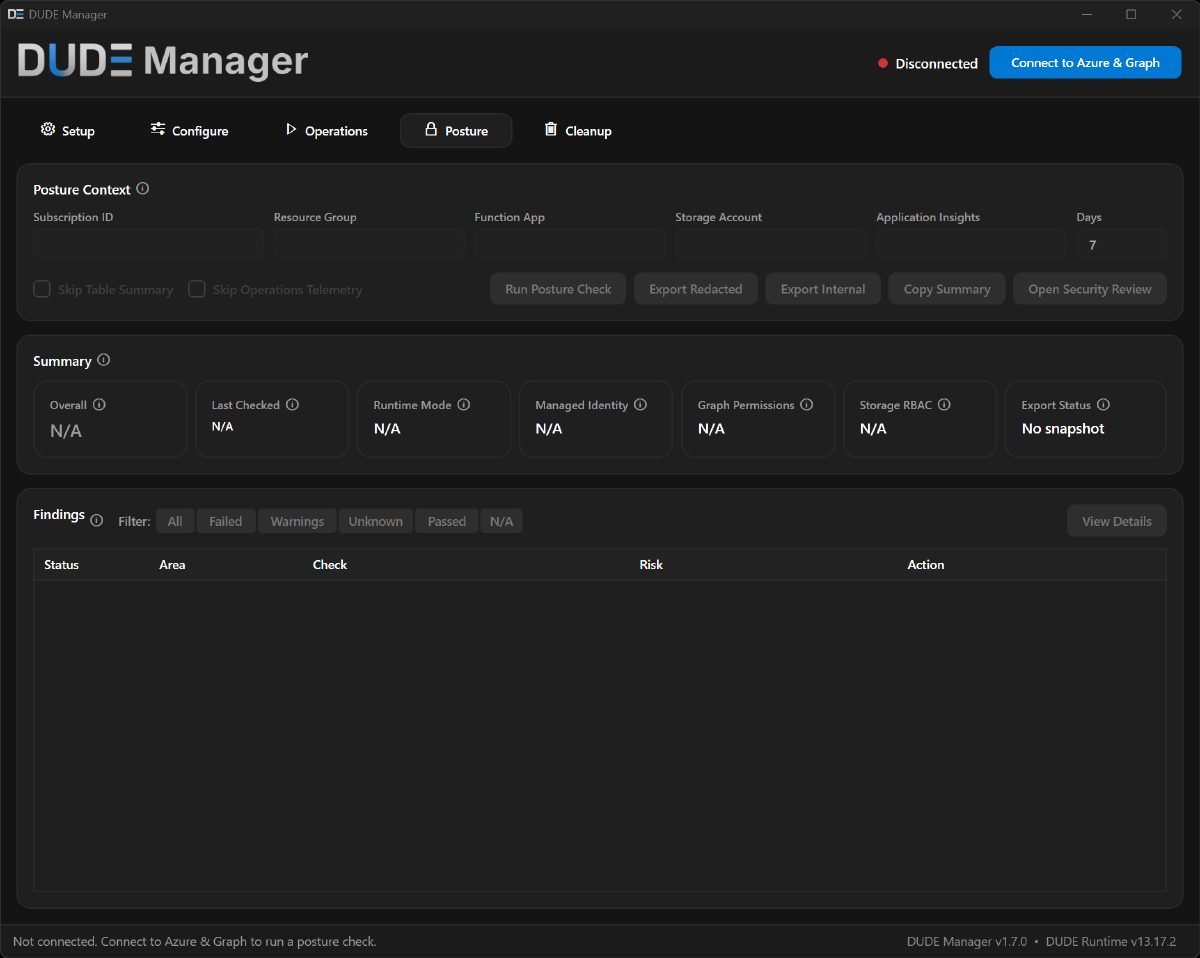
Posture — read-only findings for security review
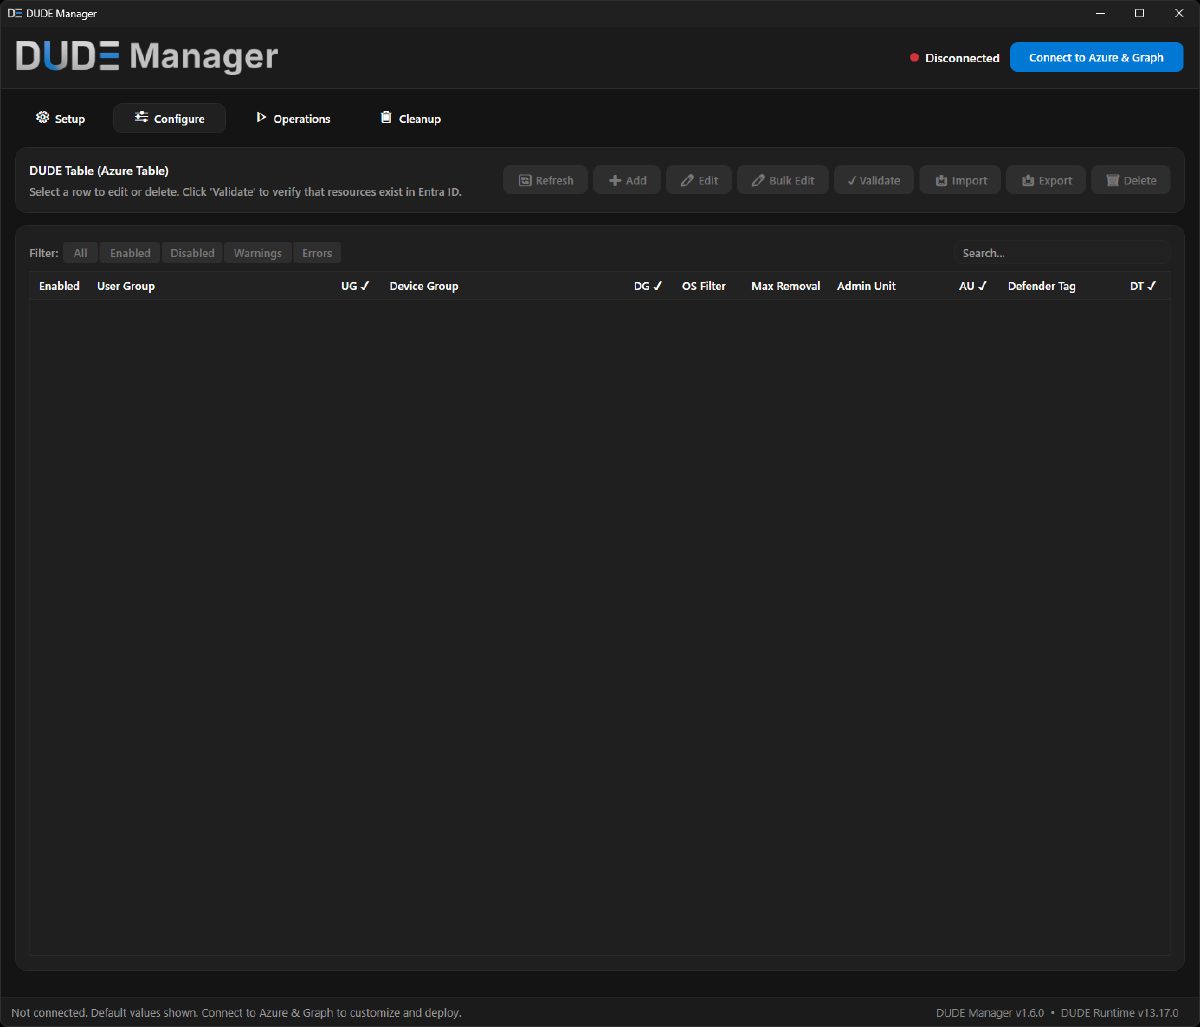
Configure — user group → device group mappings
Setup — deploy and verify the Azure resources

Writing about DUDE Manager